Find what you actually
have exposed.
AutoScan is one agentic scanner across your attack surface, apps, and code. It continuously maps what you expose to the internet, tests your running web apps and APIs, and scans your source code, then proves what is actually exploitable with real exploitation: unauthenticated APIs, open ports, TLS errors, admin panels, default credentials, IDOR, SQL injection, SSRF, and more. Every priority finding is validated and signed off by a senior security engineer in an auditor-accepted report, and in the beta ships with AI-suggested fixes. A full pentest in minutes, not once a year.
Backend launching soon · Join the waitlist for early access
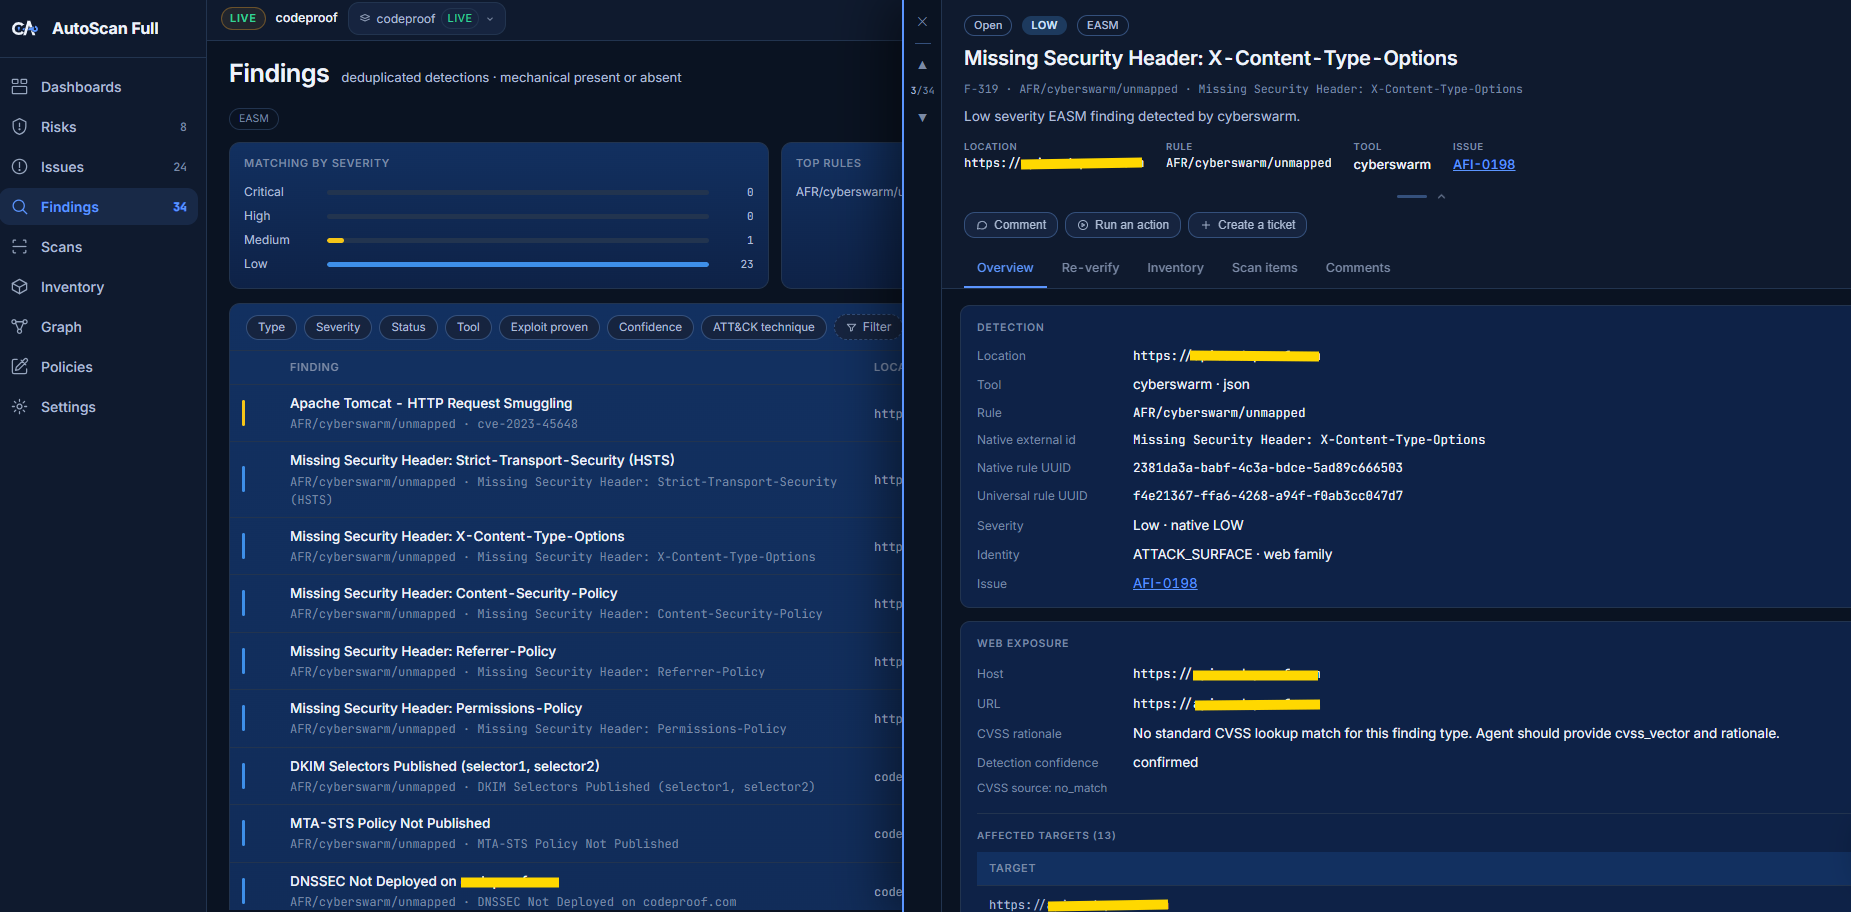
Findings deduplicated and prioritized by real exploitability, each with evidence and remediation.
One scanner, full coverage
Your attack surface, apps, and code.
One agentic scanner that covers what used to take three separate tools and a once-a-year pentest.
External Attack Surface Management
Continuously discover and test everything you expose to the internet: domains, cloud assets, APIs, and forgotten services.
Dynamic Application Security Testing
Test your running web apps and APIs the way an attacker would.
Static Application Security Testing
Scan source code for vulnerabilities before they ship.
On-demand penetration test
A full pentest in minutes, not once a year. Evidence-backed, with zero false positives.
Every finding is validated with real evidence and ships with clear, step-by-step fix instructions.
See it in action
Watch the real product.
Short screen recordings of AutoScan running against a live demo workspace. Real product, not mockups.
Scan only what you authorize
Every domain and IP range is verified and consent-based. AutoScan can only touch assets you have proven you own.
Findings, issues, and risks
The same evidence in three views: raw findings, the issues they group into, and the attack paths they add up to.
On-demand checks
Need one answer fast? Check a URL, port, TLS, DNS, or email posture on its own, without running a full scan.
How It Works
Enter a domain. We handle the rest.
No scheduling. No waiting room. No $15,000 invoice. Pentest, then verify your fixes held.
Enter a Domain and Go
Enter your domain and we handle the rest. Prove ownership with a quick DNS TXT record, the same way Google Search Console works. Optionally add IP ranges or specific subdomains to scope.
AutoScan Attacks Your Surface
AI agents orchestrate hundreds of specialized tools across thousands of assets, actively attempting exploitation, not just scanning. Default credentials tried. SQL injection payloads sent. Real evidence collected.
Auditor-Ready Report in 20 min
Executive summary plus technical findings with evidence. Every HIGH and CRITICAL finding reviewed by a senior security engineer before sign-off. SOC 2 / ISO 27001 accepted.
Fix, Then Verify
The moment you ship a fix, re-scan the selected findings to confirm each one is actually resolved. No new engagement, no extra fee. Your surface is monitored as it changes, not captured once.
Coverage
What we test.
A full agentic penetration test across your attack surface, apps, code, and the open web. Hundreds of tools orchestrated, every finding validated by real exploitation, with nightly continuous retesting as your assets change.
Leaked Credentials & Info-Stealer Intel
- Credentials in info-stealer logs
- Employee account compromise
- Breach-corpus credential matches
- Credential-spray and ATO exposure
Exposed Secrets & API Keys
- API keys and tokens in responses
- Secrets in JavaScript bundles
- Cloud credentials exposed
- Cached and archived secret leaks
Source Code & Repositories
- Public code repositories
- Secrets committed to repos
- Exposed .git directories
- Leaked internal source
Code Scanning (SAST)
- Vulnerabilities in source
- Insecure dependencies
- Hardcoded secrets in code
- Client-side JavaScript flaws
API Security
- Unauthenticated API endpoints
- Exposed OpenAPI / Swagger schemas
- Broken object-level auth (IDOR / BOLA)
- Excessive data exposure
Web Application (OWASP Top 10)
- SQL and command injection
- XSS and CSRF
- SSRF and open redirect
- Auth and session flaws
Known CVEs & Vulnerable Software
- Remotely exploitable CVEs
- Outdated components
- End-of-life software
- Default and known credentials
Network & Exposed Services
- Open port exposure
- Unprotected admin panels
- SSH / RDP / SMB / databases
- Unauthenticated services
TLS & Certificates
- Deprecated TLS 1.0 / 1.1
- Weak cipher suites
- Expired or mis-scoped certs
- Certificate name mismatch
DNS & Email Security
- Subdomain takeover
- Dangling CNAME records
- SPF / DKIM / DMARC
- DNSSEC and MTA-STS
Cloud & Infrastructure
- Public S3 / GCS buckets
- Cloud origin exposure
- IMDS credential theft
- Misconfigured storage
CORS, Headers & Config
- Permissive CORS policies
- Missing security headers
- Clickjacking and SRI gaps
- Staging and debug exposure
Real findings
What AutoScan finds.
The classes of security findings AutoScan surfaces, from leaked credentials and exposed secrets to API flaws, injection, known CVEs, and cloud misconfigurations. This is agentic penetration testing, not a vulnerability scan: findings tagged Confirmed exploited are validated with real, safe exploitation, and each ships with an AI-suggested fix.
SQL injection (SQLi)
Injectable parameters that let attackers read or alter backend databases: blind, error-based, and union-based SQLi.
Confirmed exploitedInfo-stealer credential leaks
Employee and customer logins harvested by info-stealer malware and exposed in breach data, driving account takeover (ATO).
IDOR / BOLA broken authorization
Insecure direct object references that let one account reach data belonging to other accounts through the API.
Confirmed exploitedExposed OpenAPI / Swagger schema
Unauthenticated API documentation that maps every endpoint, parameter, and method for attackers.
Confirmed exploitedExposed API keys & secrets
Live API keys, tokens, and cloud credentials leaked in responses, JavaScript bundles, and cached pages.
Confirmed exploitedSecrets in public repositories
Access tokens and internal source exposed in public code repositories, GitHub, and open .git directories.
Default & weak credentials
Admin panels and services reachable with default or guessable credentials, enabling unauthorized access.
Confirmed exploitedUnauthenticated API endpoints
APIs that return sensitive data with no authentication or authorization checks.
Confirmed exploitedExploitable CVEs & outdated software
Known, remotely exploitable CVEs in outdated or end-of-life internet-facing components.
Public cloud storage buckets
Misconfigured S3, GCS, and Azure buckets that allow anonymous listing or download of data.
Confirmed exploitedSubdomain takeover
Dangling DNS and CNAME records pointing to unclaimed cloud resources that attackers can hijack.
Weak & deprecated TLS / SSL
Deprecated TLS 1.0/1.1, weak ciphers, and expired or mis-scoped certificates.
Misconfigured CORS
Permissive cross-origin resource sharing that enables cross-site theft of authenticated data.
Confirmed exploitedExposed staging & dev environments
Non-production, debug, and admin interfaces reachable from the public internet.
Email spoofing (SPF / DKIM / DMARC)
Missing or non-enforcing email authentication that allows domain spoofing and phishing.
Missing security headers
Absent HSTS, CSP, X-Content-Type-Options, and Referrer-Policy that weaken browser-side defenses.
Representative finding categories only. Real customer data, targets, and hosts are never published.
Why Agentic AI Pentesting
AI scale. Human judgment.
Faster. Consistent. Verified.
Manual pentesting has a people problem: scarce senior talent, firms booked out months, quality that varies by tester. AutoScan runs at AI scale and routes every priority finding through a senior security engineer. Speed without giving up judgment.
AutoScan - AI Pentest
- Results in 20 minutes - No scheduling, no kickoff calls, no waiting weeks for a slot. Start now, report in 20 minutes.
- Always consistent - Every scan runs the same checks with the same rigor. No variation between testers, no bad days, no shortcuts.
- No access or trust issues - Domain verification via DNS TXT record. No VPN access, no shared credentials, no keys handed over.
- Evidence-backed, zero noise - Every finding was actively exploited. The report contains proof, not theoretical risk scores or scanner dumps.
- Senior engineer verification - Every HIGH and CRITICAL finding is reviewed and signed off by a named security engineer before the report is finalized. No AI-only findings.
- Verify your fixes with a re-scan - Ship a fix, then re-scan the selected findings to confirm each one is actually resolved. No new engagement, no extra fee, no scheduling delay.
- Comprehensive coverage and monitoring - Full external attack surface coverage, monitored continuously as your assets change. Not a one-day snapshot.
- SOC 2 / ISO 27001 accepted - Auditor-accepted PDF with scope, methodology, findings, and remediation. Built for compliance.
Traditional Manual Pentest
- 2-4 weeks to schedule - Kickoff calls, scoping meetings, NDA negotiation, and scheduling coordination before a single test runs.
- Scarce senior talent - (ISC)² estimates roughly 4M unfilled security positions globally, with offensive specialists the scarcest subset. Top firms are booked months out.
- Quality varies by tester - Skill levels differ across engagements. A junior tester on a tight deadline can miss what a senior catches.
- Significant trust exposure - You share VPN credentials, API keys, admin access, and internal architecture with a team you just met.
- Mostly offshore delivery - Many firms use offshore teams for execution. US rates, offshore delivery, less accountability.
- Re-test costs extra - Fixed a critical issue? A re-test is a new engagement. More scheduling, more cost, more delay.
- Point-in-time snapshot - A single engagement captures your posture on one day. Your attack surface changes every day.
On trust: Manual pentests require you to hand over VPN access, API keys, admin credentials, and internal network diagrams to a team you just met. AutoScan verifies ownership via a DNS record - the same mechanism Google uses. We never see your credentials, never enter your internal systems, and never touch anything you have not explicitly authorised.
Why AutoScan
Compared to the alternative.
| AutoScan | Manual pentest firm | Vuln scanner | |
|---|---|---|---|
| Time to first result | 20 minutes | 2-4 weeks | Hours |
| Price | Contact us | $15K-$50K | $5K-$50K/yr |
| Active exploitation | |||
| Human verification of priority findings | |||
| Executive summary | |||
| Re-test after fixes | Extra fee | ||
| Zero false positives | |||
| SOC 2 / ISO 27001 |
FAQ
Common questions.
Get Started
Know what attackers
can see. Right now.
Free during beta. Join early access, we respond within 1 business day.